Black-Box vs. Gray-Box vs. White-Box Penetration Testing: Which Should You Choose?
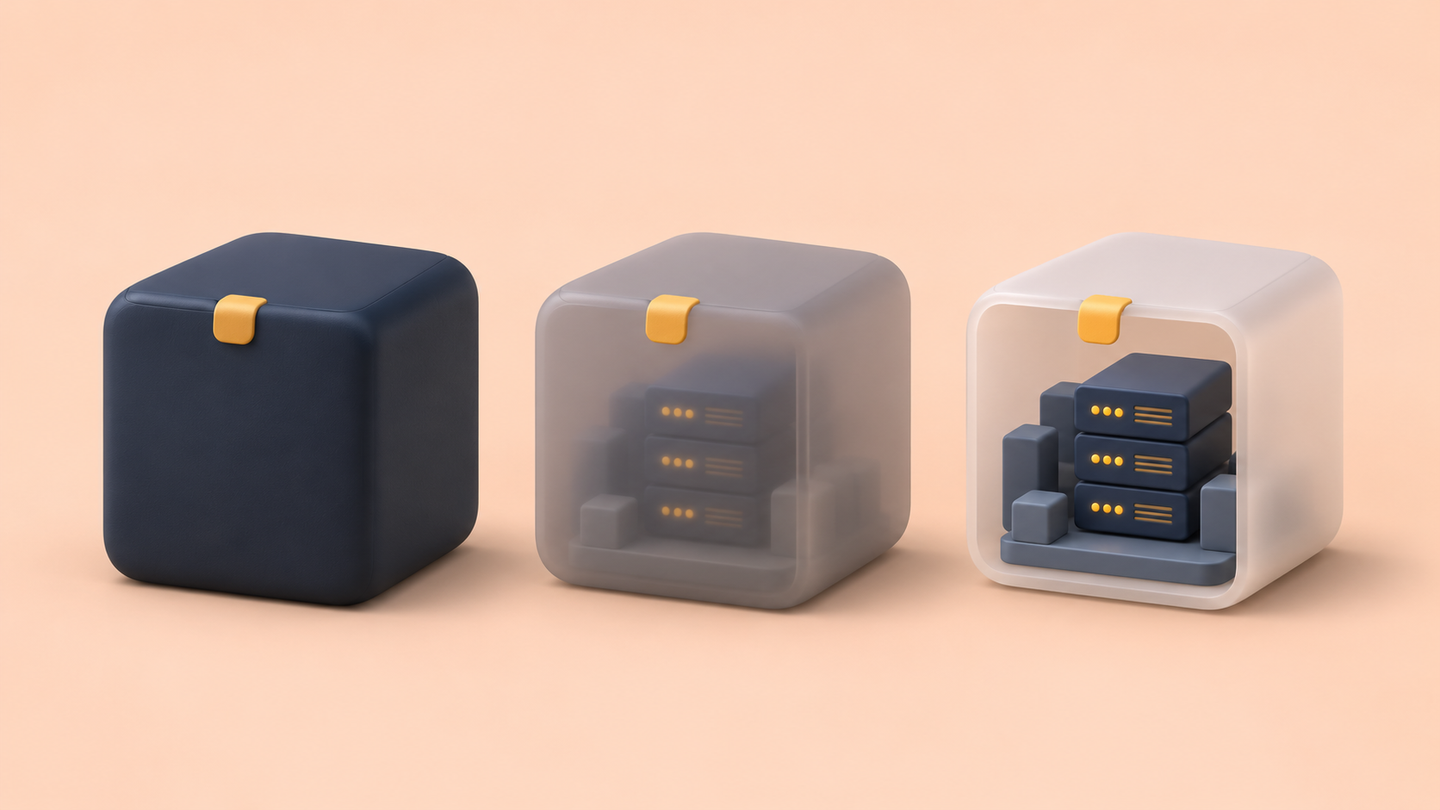
How much should your penetration testers know before they start? Giving them only a public address creates a different assessment from providing customer accounts, architecture diagrams, and source code.
Black-box penetration testing begins with little prior knowledge of the target’s internal workings. Gray-box testing provides selected information or access. White-box testing provides extensive internal information to support a more informed assessment.
The right choice depends on what you need the test to answer. Investigating what someone can discover from a public starting point requires different preparation from checking whether one customer can access another customer’s records.
Our guide to the different types of penetration testing explains which applications, networks, and other systems an assessment can cover. Black box, gray box, and white box describe the knowledge and access available while testing those systems.
Black-box vs. gray-box vs. white-box testing at a glance
| Approach | What testers typically receive | Useful when you want to… | Coverage consideration |
|---|---|---|---|
| Black box | Authorized targets and testing boundaries, with little internal information | Investigate what can be discovered and exploited from the agreed starting point | Areas requiring access may remain unexplored if testers cannot reach them |
| Gray box | Selected accounts, documentation, or environment details | Assess permissions, customer separation, and risks from a defined level of access | Coverage depends on the roles, information, and workflows supplied |
| White box | Extensive documentation, architecture details, and potentially source code or configurations | Examine how important controls are designed, implemented, and enforced | The proposal still needs to specify which materials and controls receive review |
These labels describe broad approaches. Ask the provider to identify the actual information, accounts, and review activities included in its proposal.
What is black-box penetration testing?
Black-box penetration testing gives testers little prior information about how the target works internally. They investigate what they can learn from the authorized starting point and use that knowledge to identify potential attack paths.
For a customer portal, testers might begin with its public address. They could examine exposed functionality, account registration, login and recovery flows, and information revealed by the application.
Black-box testing can be useful when discovery itself is part of the question: What could someone learn about this service without being given internal documentation?
The tradeoff is uncertainty about how far the assessment will progress. If testers cannot obtain access to restricted functionality, that functionality may receive limited coverage.
An unsuccessful attempt to get past a login page does not establish that the features behind it are secure.
Black box also does not necessarily mean unauthenticated throughout the engagement. If public registration is available and permitted, testers may create an account and investigate the access it provides. The scope should explain which activities are allowed.
What is gray-box penetration testing?
Gray-box penetration testing supplies selected knowledge or access so testers can investigate particular risks without first having to discover or obtain everything themselves.
For an application assessment, that might include:
- Accounts representing ordinary users and administrators.
- Accounts belonging to separate customer organizations.
- API documentation and test credentials.
- A walkthrough of important workflows.
- An explanation of intended permission boundaries.
Consider a portal where customers upload confidential documents. Providing accounts for two separate customers allows testers to investigate whether one customer can retrieve or change the other’s documents.
OWASP’s guidance on testing insecure direct object references recommends using multiple users to examine access to resources belonging to different accounts. This makes the expected boundaries easier to test.
Gray-box testing is useful when your concern begins with a known level of access: What could someone do with a compromised customer account? Could an employee exceed their assigned permissions?
The accounts need to match those questions. One administrator account does not provide the same testing perspective as ordinary users from different customers.
What is white-box penetration testing?
White-box penetration testing provides extensive internal information to support the assessment. Depending on the engagement, this could include source code, architecture diagrams, configuration details, documentation, and access to developers.
For the same customer portal, testers might examine the code responsible for deciding which customer owns a document, then investigate how the running application enforces that decision.
This can help connect observed behavior with its implementation. A suspicious response may lead to a targeted code review, while a weakness identified in code may guide a test against the application.
OWASP’s Web Security Testing Guide describes source code review and penetration testing as complementary techniques within a broader testing program.
White-box access still needs a defined scope. Giving a provider repository access does not establish that every file will receive a security review. Confirm whether the engagement includes targeted code inspection, a broader manual code review, configuration review, or another agreed combination.
Extensive knowledge also does not mean unrestricted permission to change systems or perform disruptive tests. Permitted activities remain part of the engagement’s rules.
Which approach should your business choose?
Start with the uncertainty you want to resolve.
Choose black box when discovery is part of the objective
A black-box approach may fit when you want to understand what testers can identify and exploit without supplied internal knowledge.
For example: “Starting from our public service address, what functionality and information can someone discover, and what could that expose?”
Discuss what should happen if the assessment does not reach authenticated features. You may want a separate phase with supplied accounts to investigate those areas.
Choose gray box when you need to examine defined access boundaries
Gray-box testing is a practical option when your priority is what users or compromised accounts can do.
For example: “Can a standard customer user export records belonging to another customer or perform an administrator’s actions?”
Supply representative accounts, realistic test data, and an explanation of the intended restrictions. OWASP’s authorization testing guidance covers examining access between different users and different privilege levels.
Choose white box when implementation details matter to the question
Discuss a white-box approach when you need closer investigation of how a sensitive control works.
For example: “We changed the authorization service used by several applications. Are the new checks implemented consistently, and can a reachable workflow bypass them?”
Identify the relevant components and agree on how testers will combine implementation review with testing of the running system.
Is black-box testing more realistic?
Black-box testing represents a particular starting condition: limited prior knowledge. That condition may fit your scenario, but attackers can also have valid accounts, stolen documentation, or knowledge accumulated over time.
A customer account can be a realistic starting point for investigating customer data exposure. Detailed implementation knowledge can help testers investigate a weakness an attacker might eventually discover.
A useful scoping question is: Which assumptions let us investigate the risk we care about within the available testing time?
You can combine approaches. An engagement might begin without supplied credentials, then continue with representative accounts. A targeted source code review could follow if implementation questions arise.
Ask the report to distinguish what testers discovered independently from what your team supplied.
Are black-box, gray-box, and white-box the same as external and internal testing?
These are separate scoping decisions.
Internal and external testing describe the network position from which an assessment operates. Black box, gray box, and white box describe the information and access provided.
An external network assessment can include detailed diagrams and configuration information. An internal assessment can begin with limited knowledge of the environment.
Likewise, providing customer credentials for an internet-facing application does not make it an internal network test.
Our guide to internal versus external penetration testing explains how network starting positions affect coverage.
How does the approach affect cost and testing time?
The label alone does not determine the price.
Discovery takes time. Supplying useful accounts and documentation can allow more of the engagement to focus on selected controls and workflows. Reviewing source code or complex architecture can add work of its own.
For the customer portal, compare what each proposal allocates time to investigate. Does it cover public entry points, multiple customer roles, supporting APIs, and implementation review? Which areas receive less attention?
Use our guide to penetration testing cost when comparing the coverage behind a quote.
Agree on access during the scoping phase
Work with your penetration testing provider to decide what information and access will help testers investigate your concerns. Discuss:
- Starting information: What testers receive and what they will need to discover.
- Accounts and roles: Which users, permission levels, and customer organizations should be represented.
- Review materials: Which documentation, source code, and configurations will support the assessment.
- Priority workflows: The actions and data boundaries that matter most to your business.
- Testing phases: Whether to begin with limited information and introduce additional access later.
- Reporting: How the report will explain the access provided, areas tested, and coverage limitations.
Your provider should explain how these choices affect coverage and document the agreed approach in the proposal.
For a broader preparation checklist, see Choosing the Right Scope for Your Next Pentest.
Discuss your testing approach with Halo Security
Start with what you want to learn about your security. Share the application or environment you want assessed, the concern prompting the test, and any customer requirements or deadlines.
Our friendly, knowledgeable penetration testers can work through your goals with you, explain the options, and help you decide what access makes sense. Together, we’ll define an assessment with clear coverage and useful results for your team.
Discuss your penetration testing needs with Halo Security.
FAQ
What is the main difference between black-box, gray-box, and white-box penetration testing?
The main difference is the information and access supplied to testers. Black-box testing begins with little internal knowledge. Gray-box testing provides selected information or access. White-box testing provides extensive internal information. The scope should name the actual accounts, materials, and activities included.
Which penetration testing approach is best for a SaaS application?
For questions about customer separation and user permissions, discuss gray-box testing with representative accounts from different customer organizations and permission levels. White-box access may support deeper investigation of implementation details. Public entry points can also receive testing without supplied credentials.
Does white-box penetration testing include source code review?
It can, but confirm the extent of review in the proposal. Repository access alone does not establish that the provider will review the entire codebase. Ask which components receive review and how that work connects to testing the running application.
Can one engagement combine black-box and gray-box testing?
Yes. An engagement can begin with limited information and later introduce accounts or documentation. Agree on the phases beforehand and ask the report to distinguish independently obtained access from access your team supplied.
Is gray-box testing the same as authenticated testing?
The terms overlap, but describe different things. Authenticated testing uses a logged-in session or valid credentials. Gray-box testing describes selected prior knowledge or access, which may include credentials, documentation, or environment details.