Blog
  • Home
  • Login
  • Try It
Two Years Running: What Winning MSP Today Product of the Year Means to Our Partners

Two Years Running: What Winning MSP Today Product of the Year Means to Our Partners

Partners • 4 min read
Halo Security Wins 2026 MSP Today Product of the Year Award

Halo Security Wins 2026 MSP Today Product of the Year Award

Announcements • 2 min read
CVE-2026-48172: Critical LiteSpeed cPanel Plugin Flaw Under Active Exploitation

CVE-2026-48172: Critical LiteSpeed cPanel Plugin Flaw Under Active Exploitation

Threat Advisories • 7 min read
How to Prepare for Your First PCI ASV Scan (and Avoid the Most Common Failures)

How to Prepare for Your First PCI ASV Scan (and Avoid the Most Common Failures)

PCI Compliance • 9 min read
Critical Cisco Catalyst SD-WAN Auth Bypass (CVE-2026-20182) Under Active Exploitation

Critical Cisco Catalyst SD-WAN Auth Bypass (CVE-2026-20182) Under Active Exploitation

Threat Advisories • 4 min read
CISA BOD 26-02 and the Risk of Unsupported Edge Devices: What Security Leaders Should Take From It

CISA BOD 26-02 and the Risk of Unsupported Edge Devices: What Security Leaders Should Take From It

Attack Surface Management • 7 min read
CVE-2026-0300: Critical PAN-OS Zero-Day Hands Attackers Root on Exposed Firewalls

CVE-2026-0300: Critical PAN-OS Zero-Day Hands Attackers Root on Exposed Firewalls

Threat Advisories • 5 min read
PCI ASV Scanning vs. PCI Penetration Testing: Which Do You Need (and When Do You Need Both)?

PCI ASV Scanning vs. PCI Penetration Testing: Which Do You Need (and When Do You Need Both)?

PCI Compliance • 8 min read
CVE-2026-41940: Critical cPanel & WHM Authentication Bypass Under Active Exploitation

CVE-2026-41940: Critical cPanel & WHM Authentication Bypass Under Active Exploitation

Threat Advisories • 5 min read
How to Choose a PCI ASV: 7 Questions to Ask Before You Sign

How to Choose a PCI ASV: 7 Questions to Ask Before You Sign

PCI Compliance • 6 min read
NIST Vulnerability Shift: How the New Model Impacts Your Security Strategy and How to Adapt

NIST Vulnerability Shift: How the New Model Impacts Your Security Strategy and How to Adapt

Risks & Vulnerabilities • 5 min read
How to Affordably Cut Your External Attack Surface Risk in 30 Days Without Adding Headcount

How to Affordably Cut Your External Attack Surface Risk in 30 Days Without Adding Headcount

Attack Surface Management • 5 min read
TLS Certificate News: Certificate Lifetimes Shrinking to 47 Days

TLS Certificate News: Certificate Lifetimes Shrinking to 47 Days

Cybersecurity • 3 min read
Halo Security Achieves SOC 2 Type II Compliance: Proving Security Excellence Over Time

Halo Security Achieves SOC 2 Type II Compliance: Proving Security Excellence Over Time

Announcements • 2 min read
The MSP's Guide to External Attack Surface Management

The MSP's Guide to External Attack Surface Management

Partners • 3 min read
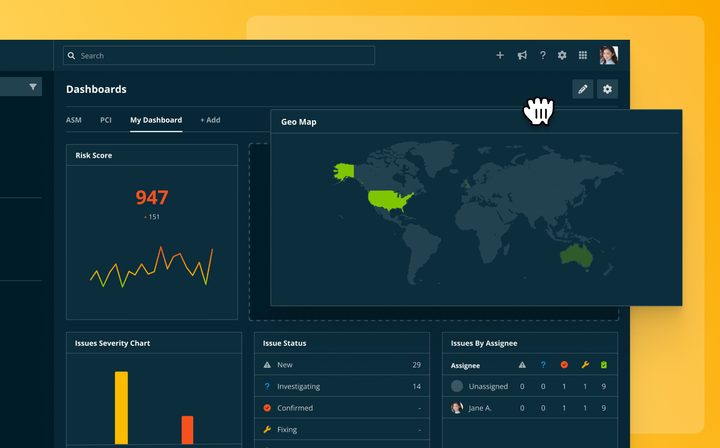
Introducing Custom Dashboards and Reports

Introducing Custom Dashboards and Reports

Announcements • 3 min read
← Newer Posts Older Posts →
Penetration Testing
  • Penetration Testing
  • Web Application
  • Mobile Application
  • API
  • External Network
  • Internal Network
  • Wireless
  • Compliance
  • Social Engineering
  • Red Teaming
  • Scope a Pentest
Platform
  • Attack Surface Management
  • Vulnerability Scanning
  • PCI Compliance
  • Dark Web Monitoring
  • Use Cases
  • Features
  • Integrations
  • Plans & Pricing
  • Free Trial
Resources
  • Resources
  • Docs
  • Support
  • Blog
  • PCI Glossary
  • CVE Advisories
  • Guides
  • Site Scan
Company
  • About Us
  • Customers
  • News
  • Partner List
  • Become a Partner
  • System Status
  • Trust Center
  • Contact
  • Leader on G2
  • Users Love Us on G2
  • BBB Accredited Business, A+ rating
  • CREST Pathway+ organisation
  • MSP Today Product of the Year 2026
  • AICPA SOC

A CREST Pathway+ organisation has signed Codes of Conduct and Ethics and self-assessed against CREST’s standards. A CREST Pathway+ organisation is aiming for but is not a CREST Accredited Member company.

© 2026 Halo Security
  • Terms
  • Privacy
  • Cookie Preferences